

The Vulnerability Landscape: Why Windows RDP Servers Are Prime Targets
In short: Good RDP security means changing the default port 3389, using strong passwords with account lockout, turning on Network Level Authentication, limiting access by IP in the firewall and keeping Windows updated. These steps stop most brute-force attacks.
Windows Remote Desktop Protocol (RDP) is one of the most widely deployed remote workstation administration technologies globally. Unfortunately, its popularity also makes it the number one target for automated threat actors, credential-stuffing botnets, and ransomware syndicates. Within minutes of provisioning a new Windows Server with an exposed public IP address, automated scanners begin bombarding default port 3389 with tens of thousands of username and password combinations. If your server utilizes the default Administrator username and a common password without network-level authentication, account takeover is virtually inevitable.
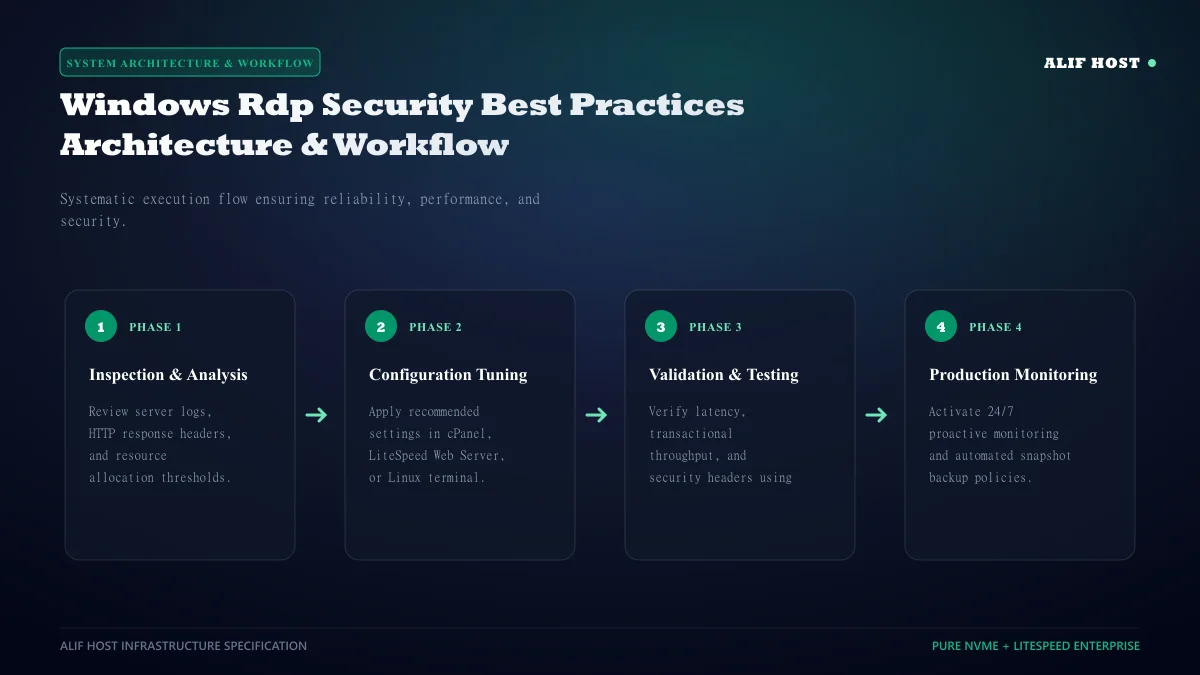
- Continuous Automated Port Sweeps: Global botnets sweep the entire IPv4 address space continuously looking for listening port 3389.
- Ransomware Gateway: Over 60% of commercial ransomware intrusions originate from compromised remote desktop credentials.
- Resource Saturation: Even if attackers fail to guess your password, thousands of concurrent connection handshakes exhaust server CPU and network bandwidth.
Action 1: Enforce Network Level Authentication (NLA)
Network Level Authentication (NLA) is a critical defensive protocol that requires the connecting user to authenticate their credentials with the Windows security subsystem before the server establishes a full Remote Desktop session or loads the visual desktop screen.
- Prevents Denial of Service: Blocks unauthenticated attackers from exhausting server RAM with open desktop display sessions.
- How to Enable: Open
System Properties->Remotetab -> Check "Allow connections only from computers running Remote Desktop with Network Level Authentication (recommended)".
Action 2: Change the Default RDP Port (Port 3389)
Automated brute-force bots scan standard default port 3389 exclusively. Changing your listening port to a non-standard custom port (between 49152 and 65535) immediately eliminates 98% of indiscriminate background bot noise.
Registry Modification Workflow
Launch regedit.exe and navigate to: HKEY_LOCAL_MACHINE\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp. Locate PortNumber, select "Decimal", and change the value to your custom port (e.g. 52840).
Firewall Rule Creation
CRITICAL: Before restarting the Remote Desktop service, create an Inbound Rule inside Windows Defender Firewall allowing TCP traffic on your new custom port number, otherwise you will be locked out.
Comparison: RDP Security Hardening Matrix
Review the technical effectiveness of key RDP defensive controls.
| Security Control | Implementation Mechanism | Threat Mitigated | Effectiveness |
|---|---|---|---|
| Network Level Authentication (NLA) | System Remote Settings | Pre-session resource exhaustion & exploit probes | High |
| Custom RDP Port | Windows Registry + Firewall | Automated indiscriminate port 3389 scanners | High |
| Account Lockout Threshold | Local Security Policy (secpol.msc) | Continuous dictionary brute-force attacks | Maximum |
| IP Address Whitelisting | Windows Defender Firewall Rule | All unauthorized external network connections | Maximum (Enterprise Standard) |
| Two-Factor Authentication (2FA) | Duo Security / Entra ID MFA | Stolen or leaked administrator passwords | Maximum |
Action 3: Configure Account Lockout Policies in secpol.msc
By default, Windows Server allows unlimited consecutive incorrect password attempts, enabling automated botnets to test dictionary files indefinitely. Stop this by configuring local security policies:
- Run
secpol.mscto launch Local Security Policy. - Navigate to Account Policies -> Account Lockout Policy.
- Set "Account lockout threshold" to 5 invalid logon attempts.
- Set "Account lockout duration" to 30 minutes.
- Set "Reset account lockout counter after" to 30 minutes.
Action 4: Restrict RDP Access via Firewall IP Whitelisting
The most impregnable defense for a remote desktop server is IP whitelisting. If you possess a static IP address at your office or home, configure Windows Defender Firewall to allow inbound connections on your RDP port ONLY from your specific IP address, automatically dropping all connection attempts from the rest of the worldwide internet.
Automated Intrusion Defense with Software Intrusion Prevention (IPBan)
While changing ports reduces automated noise, determined attackers still probe custom ports. Deploying an automated host intrusion prevention service like IPBan on Windows Server delivers fail2ban-equivalent protection:
- Event Log Auditing: IPBan continuously monitors the Windows Security Event Log for Event ID 4625 (An account failed to log on).
- Automated Firewall Blocking: When an IP address exceeds five failed authentication attempts within 15 minutes, IPBan dynamically creates a Windows Defender Firewall rule blocking that IP for 24 hours.
Enforcing Group Policy Objects (GPO) for Administrative Session Limits
Orphaned or disconnected RDP sessions can remain active in server memory for days, holding open database connections and sensitive documents. Configure Group Policies (gpedit.msc -> Computer Configuration -> Administrative Templates -> Windows Components -> Remote Desktop Services -> Remote Desktop Session Host -> Session Time Limits) to automatically terminate disconnected sessions after 30 minutes.
Enforcing Multi-Factor Authentication (MFA) on Windows RDP Sessions
Deploying Duo Security or Microsoft Entra ID Multi-Factor Authentication (MFA) on your Windows RDP server ensures that even if an attacker successfully guesses or compromises your administrator password, they cannot establish a desktop session without approving a push notification on your physical smartphone.
Windows RDP Hardening Audit Checklist: 5 Essential Security Controls
Before deploying a Windows RDP server for live commercial tasks, ensure these five security controls are actively verified:
- Verify Network Level Authentication (NLA): Confirm NLA is enforced in Remote Desktop system properties.
- Confirm Custom RDP Port: Verify the listening port has been changed from 3389 and allowed through Windows Firewall.
- Audit Account Lockout Policies: Ensure
secpol.msclocks out accounts after 5 invalid logon attempts. - Deploy Strong Alphanumeric Passphrases: Enforce complex 20+ character passphrases containing upper/lower/numbers/symbols.
- Restrict IP Access Where Possible: Whitelist trusted office or home static IPs in Windows Defender Firewall rules.